

“A lot of back and forth before this was finally released, so this is not going to be we’re not going to go down to every control and talk about every change it’s made, but it is kind of a high-level overview of some of the biggest changes not only from what was changed in the controls and responsibilities but also some of the things that from an assessment standpoint that assessors have to worry about as well kind of pulls back the current a little bit we need to do it so if you are an entity that needs to be PCI Compliant you’re going to learn a little bit about the changes made to not only your responsibilities but ours as well.”
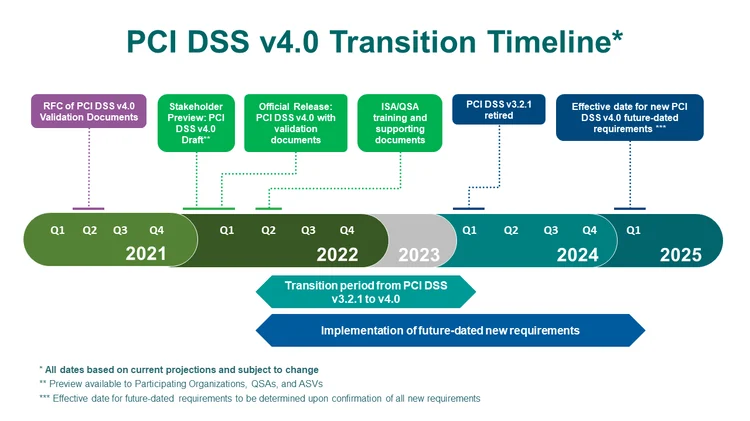
PCI 4.0 Timeline for Implementation
Though PCI DSS 4.0 was released in March 2022, most requirements don’t take effect immediately. The PCI Security Standards Council set the formal transition and compliance date for PCI DSS 4.0 as March 31, 2025. Certain controls must be implemented as soon as you start using PCI DSS 4.0, but the bulk are considered “best practices” until 2025.
Get Ready for PCI DSS 4.0: Key Changes You Need to Know
PCI DSS 4.0 is arriving soon with a compliance deadline of March 2025. While you still have some time, businesses should start preparing now for some important updates to the Payment Card Industry Data Security Standard (PCI DSS). In this post, we’ll overview a few of the most impactful modifications you can expect in PCI DSS Version 4.0.
Key Changes to Get Ready For
While PCI DSS 4.0 retains many legacy requirements, it also contains significant new mandates. Here are some to prioritize for the next three years:
Strict Role and Responsibility Definitions
Merchants and service providers will need to formally assign “who’s who” for security controls in the documentation. Clear roles and responsibilities must encompass Requirements 1-12.
Universal Multi-Factor Authentication (MFA)
Whereas MFA was previously only required for remote access, PCI DSS 4.0 will demand it for any personnel accessing cardholder data systems. This includes internal staff in addition to remote workers.
Internal Pen Testing and Vulnerability Scans
All merchants and service providers must implement credentialed vulnerability scans for Internet-facing and internal networks. Approved scanning vendors (ASVs) typically conduct external scans, but internal scans to find vulnerabilities require extra care and planning.
Annual Scoping Exercises
PCI DSS has always necessitated that your cardholder data environment be well-understood. However, with PCI DSS 4.0 merchants must provide and continually update documentation detailing exactly how payment data flows through their people, processes, and technical systems.
Extra Visibility for QSAs
If your business is required to undergo assessments by a qualified security assessor (QSA), you can anticipate providing more detailed paperwork in PCI DSS 4.0. QSAs must tie evidence to each requirement, including documenting who they interviewed and what specific documentation satisfies controls.
Get a Head Start on PCI DSS 4.0
This article summarizes only a sample of coming PCI DSS 4.0 upgrades. Now is the time to scrutinize PCI DSS 4.0’s specific requirements against your business functions. Identify potential gaps that will require financial, technological, or operational resources to fix before 2025 arrives. By planning ahead, you’ll retain ample time to budget for resources and get a jumpstart on implementation.

Related Content

AI and Cybersecurity: Navigating Promise and Pitfalls
